

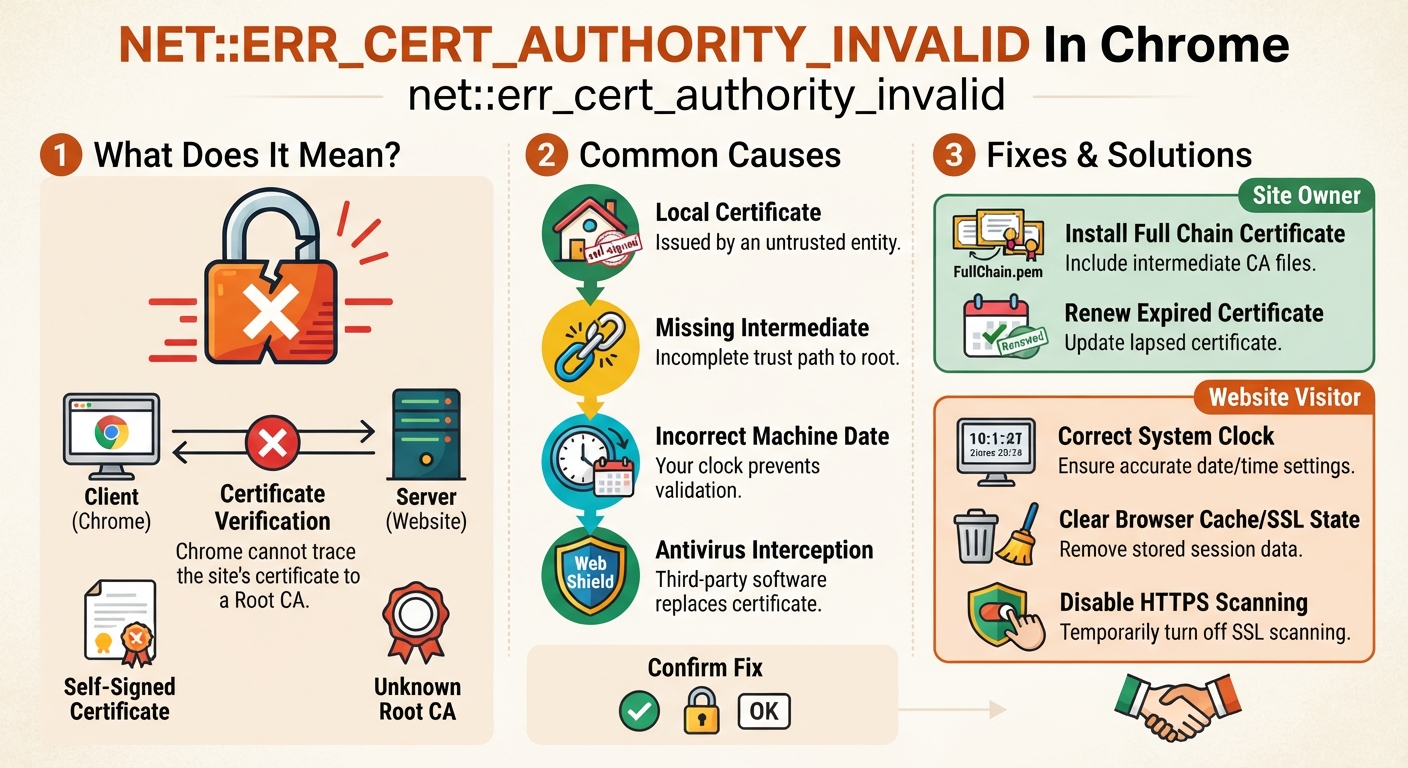
Chrome stops the page, shows “Your connection is not private”, and prints net::err_cert_authority_invalid underneath. The notice adds that the server could not prove it is example.com, because its security certificate is not trusted by your operating system.
Nothing was broken into. Chrome cannot trace the certificate back to a root it recognises. Who repairs it depends on whether you run the site or only wanted to read it.
What NET::ERR_CERT_AUTHORITY_INVALID Means
Chrome measures every certificate against its trust store. Windows and macOS hand over root CAs from the operating system. Linux builds read the Chrome Root Store instead.
One broken step in that path ends the handshake before any data moves. The certificate itself can be perfectly valid and still fail, which is why HTTPS and its trust model deserve a closer look in this guide to encryption on Linux systems.
| You are | Start here |
|---|---|
| The owner | Run openssl s_client -connect yourdomain.com:443 -servername yourdomain.com 2>/dev/null | openssl x509 -noout -issuer -dates -subject. It names the signer, the validity window and the covered domain. |
| A reader | Correct the taskbar clock through Settings, Time & Language, Sync now. Open Ctrl+Shift+N; if the page loads privately, wipe the cache. Switch off SSL scanning in Avast, Kaspersky, ESET or Bitdefender. |
When none of those three moves change anything, the fault sits on the server and only its owner can clear it.
Seven Causes Of The Certificate Authority Error
| Cause | Proof | Repair |
|---|---|---|
| Locally made certificate, signed by nobody public | openssl x509 -noout -issuer -subject prints an identical issuer and subject | Owners swap in a free Let’s Encrypt file: sudo apt install certbot python3-certbot-nginx, then sudo certbot --nginx -d yourdomain.com -d www.yourdomain.com. Developers may import an exported PEM through certutil -addstore "Root" or update-ca-certificates, never on a live box |
| Absent middle certificate, so no path reaches a root | Counting the chain with grep -c "s:.*" returns one entry | Nginx: cat yourdomain.pem intermediate.pem > fullchain.pem, aim ssl_certificate at that bundle, then sudo nginx -t && sudo systemctl reload nginx. Apache users add SSLCertificateChainFile and run apachectl configtest |
| Lapsed leaf or middle file | openssl x509 -noout -dates shows a past notAfter | sudo certbot renew --force-renewal, then reload the daemon. Paid CAs need a fresh CSR and reissue. Set alarms 30, 14 and 7 days early |
| Unrecognised signer, such as Active Directory Certificate Services roots or dropped Symantec and GeoTrust roots | The issuer field names something other than DigiCert, Let’s Encrypt, Sectigo or GlobalSign | Push the private root to every workstation through Group Policy, Keychain or update-ca-trust. A root dropped by the Chrome Root Program forces a brand new certificate |
| Wrong machine date, which hides valid windows | Your clock differs from any online clock by minutes | Windows w32tm /resync /force; Linux sudo timedatectl set-ntp true; macOS ticks automatic date and time |
| Scanner in the middle re-signing traffic | The issuer reads “Avast Web Shield” or “Kaspersky Anti-Virus Personal Root Certificate” | Disable HTTPS scanning in Avast Core Shields, Kaspersky Network Settings, ESET SSL/TLS filtering or Bitdefender encrypted web scan, then relaunch through chrome://restart |
| Stale stored session kept after the host is corrected | The page breaks after a confirmed server repair | Flush SSL state with inetcpl.cpl, clear files with Ctrl+Shift+Delete, empty the host cache at chrome://net-internals/#dns |
Fixing ERR_CERT_AUTHORITY_INVALID On Your Own Machine
Old stored data drives a surprising share of browser puzzles, and the same habit fixes the ERR_CACHE_MISS message in Chrome. Lookup faults form a different family, covered in this walkthrough of DNS resolution failures.
Extensions matter too. A privacy add-on that rewrites requests can interfere with the handshake, so test with the ones listed among these privacy extensions for Chromium browsers switched off one at a time.
How Site Owners Repair The Trust Chain
Certbot users must load fullchain.pem. Pointing at cert.pem ships the leaf alone, and Android or Linux visitors then see the block while Windows visitors do not.
Reload the daemon after every change. A silent server that accepts connections and returns nothing points at a separate problem, described in this note on blank pages and ERR_EMPTY_RESPONSE.
Filtering hardware also re-signs traffic on its way through. Anyone running one should read how open source web application firewalls handle TLS termination before blaming the certificate.
| Pattern | Probable trigger | Responsible party |
|---|---|---|
| One site breaks, other HTTPS pages open | Server side | Owner |
| Many sites break at once | Clock, scanner or network | Reader |
| A private window loads it | Stored data or an add-on | Reader clears cache |
| Issuer field names your scanner | Interception | Reader disables scanning |
| Company portal breaks | Private root missing | IT staff |
| Broke right after reissue | Middle file absent or wrong path | Owner |
Confirming The Fix Worked
Grep the handshake for Verify return code. Zero (ok) means success. Print the whole path with -showcerts 2>/dev/null | grep -E "s:|i:", then probe from outside using curl -I https://yourdomain.com.
Retest privately and on a phone to rule out local storage. Building that habit into a wider routine is the point of FOSS Post’s privacy and security series for Linux users.
A different code means a different problem. When the signer checks out but the hostname does not, you are looking at ERR_CERT_COMMON_NAME_INVALID instead.
FAQs
What does NET::ERR_CERT_AUTHORITY_INVALID mean?
Chrome could not link a site’s certificate to a root authority it trusts. The certificate may be self-signed, missing its intermediate file, or issued by a CA outside Chrome’s trust store.
How do I fix NET::ERR_CERT_AUTHORITY_INVALID in Chrome?
Correct the system clock, open the page in Incognito, clear cached files, and switch off HTTPS scanning in your antivirus. If one site alone fails, the owner must reinstall the full chain.
Why does Reddit blame antivirus software for this error?
Reddit threads on r/techsupport keep tracing it to Avast, Kaspersky or ESET re-signing HTTPS traffic with their own root. The issuer field names the scanner, which settles the question.
Is clicking Advanced then Proceed safe, as Reddit suggests?
Only on a machine you control, such as a test box. Traffic stays encrypted but unverified, so Reddit moderators warn against it for banking, mail or any login page.
Does this error affect search rankings?
Indirectly. Crawlers blocked by the warning cannot index pages, and readers leave at once. Google usually revisits within hours of a repair, so positions recover quickly.
